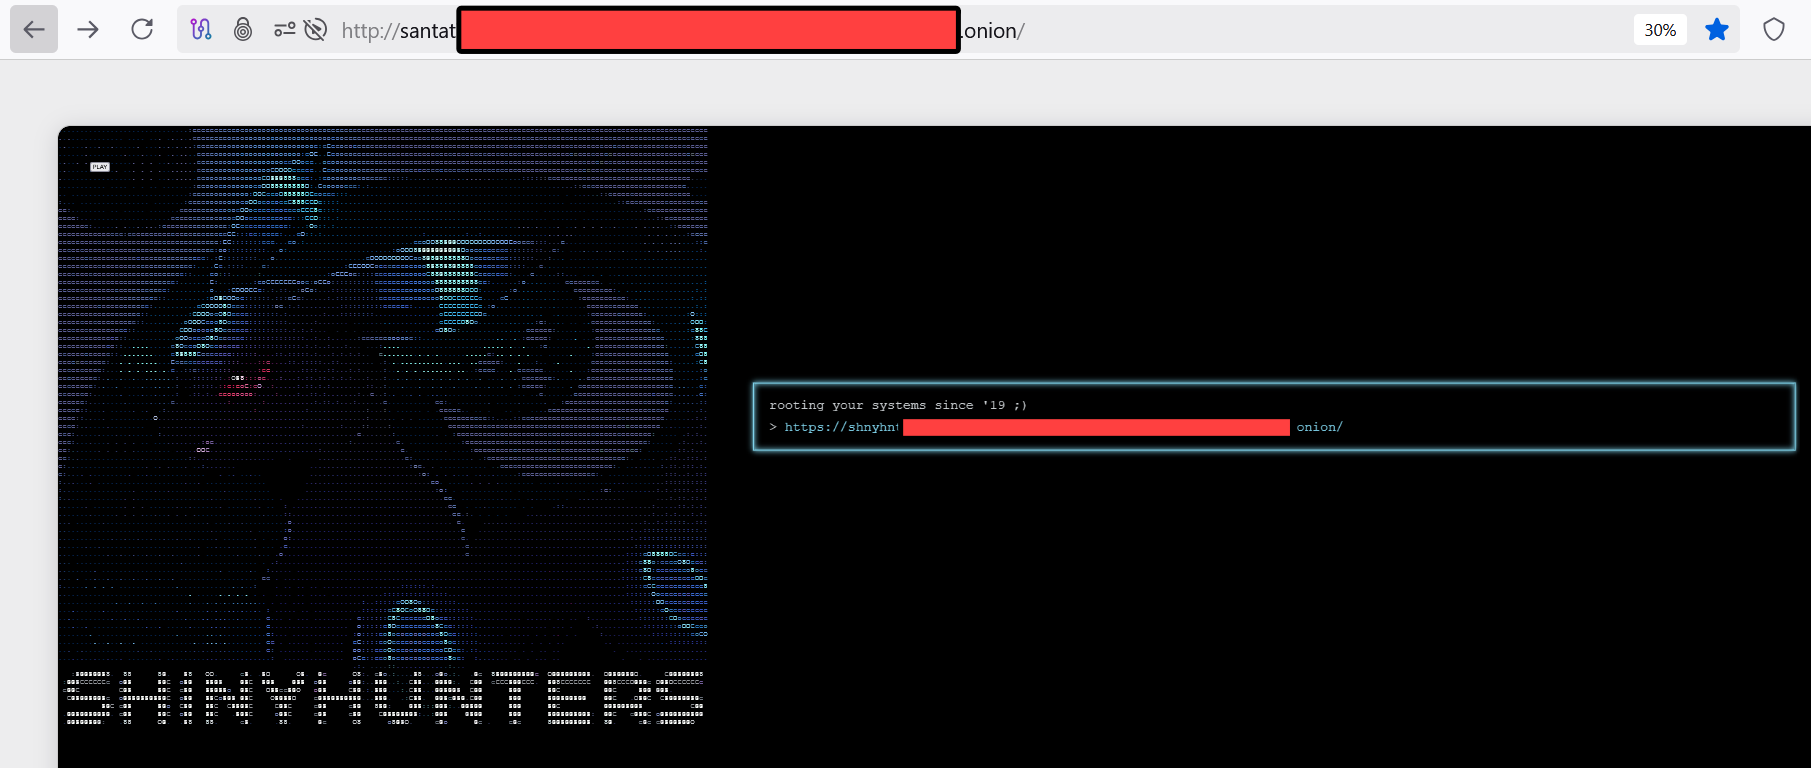
The ShinyHunters extortion group has hacked and defaced the dark web leak site operated by the Clop ransomware gang, replacing the site’s content with its own branding and a message directed at visitors.
UPDATE, September 21, 2026: ShinyHunters has escalated its dispute with Clop, demanding an eight-figure payment, threatening to disclose information about companies that allegedly paid Clop during its Oracle E-Business Suite campaign, and adding a demand for a public apology. ShinyHunters also told Hackread.com that the temporary outage affecting its own onion site was caused by unrelated network issues.
Hackread.com observed the defacement on Clop’s Tor site on September 19, 2026. The page displayed ASCII artwork associated with ShinyHunters, a link directing visitors to the group’s own site, and the message “rooting your systems since ’19 ;).”
Clop, also written as Cl0p, operates a Tor-based leak site used to name organizations targeted in its data theft and extortion campaigns. The incident is unusual because the target is itself a major cybercrime operation.
The attack appears to have started on Friday night, September 18. ShinyHunters claims it found an unauthenticated file-upload vulnerability in the Grav content management system used by Clop’s leak site. The compromise later progressed into the full defacement observed by Hackread.com.
Extent of Clop Site Compromise Remains Unclear
The visible defacement shows that whoever carried out the attack gained sufficient access to alter content served through Clop’s onion site. However, the defacement alone does not establish how deeply the underlying server was compromised or what data may have been accessed.
Hackread.com contacted ShinyHunters directly to ask how the group gained access, whether data was taken from Clop’s infrastructure and whether it obtained control of any additional systems. ShinyHunters subsequently responded to Hackread.com regarding the temporary outage affecting its own onion site but did not address these questions.
ShinyHunters Site Returns After Brief Outage
ShinyHunters’ own onion site, which was unavailable for several hours during the Clop incident, came back online later the same day. Hackread.com had asked the group whether the outage was connected to its attack on Clop or caused by a separate issue.
ShinyHunters responded that the outage was unrelated to the Clop incident. “Our onion domain is accessible. Please try a new circuit. There was a few hour downtime due to network issues that are not related to the Clop incident,” the group told Hackread.com.
The group added that it was dealing with “routine and schedule maintenance” on its infrastructure. ShinyHunters did not address Hackread.com’s other questions about how deeply it had compromised Clop’s infrastructure, whether it had taken data, or whether it controlled additional systems.
ShinyHunters Escalates Demands Against Clop
Since the original defacement, ShinyHunters has turned the compromised Clop site into a platform for making escalating demands against the ransomware group.
In its September 19 message, ShinyHunters demanded what it described as an eight-figure payment from Clop. On September 20, the group updated the message and demanded money it claims Clop earned from its Oracle E-Business Suite campaign, along with additional payment and interest.
ShinyHunters also threatened to release information it claims to possess about companies that paid Clop, including the amounts paid and Bitcoin addresses allegedly used for the transactions. Hackread.com has not independently verified those claims.
The message was updated again on September 21. ShinyHunters said its demands would increase for every 24 hours that Clop failed to engage and added another condition: a public apology issued directly to ShinyHunters.
The continuing updates indicate that ShinyHunters still has the ability to publish content through the compromised Clop site. However, they do not by themselves establish whether the group has obtained Clop’s internal data or gained access to infrastructure other than the leak site.
Clop’s Onion Site Remains Compromised
Clop’s leak site is an important part of its extortion operation, where the ransomware group names targeted organizations and publishes stolen information when its demands are not met.
Losing control of the site, even temporarily, can damage Clop’s reputation while disrupting one of the main channels it uses to publish victim data and information about its attacks.
Clop has been responsible for some of the largest mass data-theft campaigns in recent years, frequently exploiting vulnerabilities in widely used enterprise file-transfer products. Its 2023 campaign against Progress Software’s MOVEit Transfer exploited CVE-2023-34362 to steal data from exposed systems.
The MOVEit campaign alone affected more than 2,000 organizations and tens of millions of people, with victims spanning businesses, universities and government organizations. Earlier in 2023, Clop also claimed to have stolen data from approximately 130 organizations in just 10 days by exploiting a zero-day vulnerability in GoAnywhere MFT.
The FBI and CISA also linked (PDF) Clop to the MOVEit campaign and noted that the group had previously targeted Accellion FTA using similar tactics.
As of September 21, ShinyHunters continued to publish messages directed at Clop through the compromised leak site, with its latest update increasing the demands and calling for a public apology.
Click Here For The Original Source.